IT services that meet your requirements
IT services &
Modern Workplace
We look after workstations, Microsoft 365, Defender and monitoring for companies. Clear responsibilities and processes ensure stable operations.
How we organise your IT support
Outages, outdated systems and unclear responsibilities put a strain on ongoing operations. We document your environment, prioritise risks and agree on maintenance, support and escalation paths. Our information security management is certified to ISO 27001.
Information security management in accordance with ISO 27001 and documented quality processes
Microsoft 365 and Copilot with agreed permissions and governance
Monitoring and logging with Grafana, Prometheus, Loki and Alloy
Protection for clients and servers with Microsoft Defender and EDR
Orderly handover of access, documentation and systems
Personal support with agreed responsibilities and response procedures
Our services
Building blocks for stable IT operations
Working methods and certification
Transparent support instead of knowledge silos
We record systems, responsibilities and changes in shared documentation. Maintenance windows, approvals and escalations are agreed in advance. Monitoring provides the signals your operations actually need.
Our ISO 27001 processes provide a binding framework for this. They do not replace coordination, but make decisions and security measures traceable.

WAF rules as code, meaningful monitoring
We maintain Web Application Firewall rules as code, versioned and with a test environment, rather than as a click in a console. A rule hierarchy distinguishes internal services, known search engine crawlers and suspicious access patterns, with separate priorities for allowing, throttling and blocking. The correct address behind proxies and content delivery networks is crucial: evaluating the address of the upstream system instead of the actual visitor ultimately locks out your own application.
We also keep track of traffic that is not a page in a browser: API and JSON requests count too, not just page views. A simple per-address limit does little to stop traffic distributed across many individual addresses; edge caching and analysis that recognises patterns across multiple addresses are more effective. We run this analysis on a regular schedule, rather than raising an immediate alert for every deviation; actual alerts remain limited to clearly defined thresholds.
We retain logs in two stages: compressed and at low cost for the agreed retention period, with only selected anomalies that have already been reviewed feeding into a central security system. A significant event is followed by a post-mortem: what happened, which rule helped and what this means for the next configuration.

HYDRO
Connecting systems and processes
KIND
SharePoint migration

Linde
Company intranet
SharePoint Online intranet for Linde with a hub structure, custom web parts, personalised news and assisted content migration.

Linde
Making business capabilities visible
FLEX-IT for Linde: interactive tree diagram for business capabilities and IT processes, process editing and data integration.
Linde
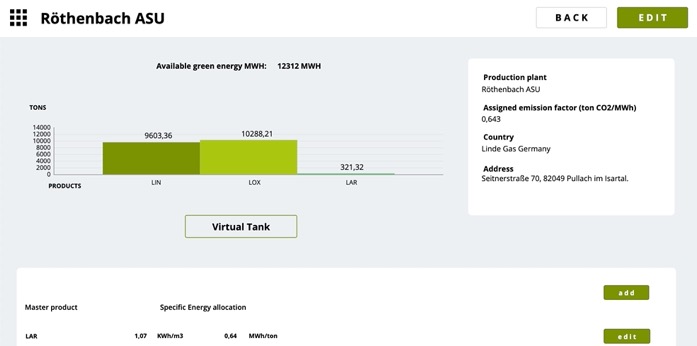
Proving the origin of certificates
Certificate management for Linde with a database and digital proof of origin in the automotive industry.

Simon-Kucher
